 Launch Receipts
Argusred
argusred.com
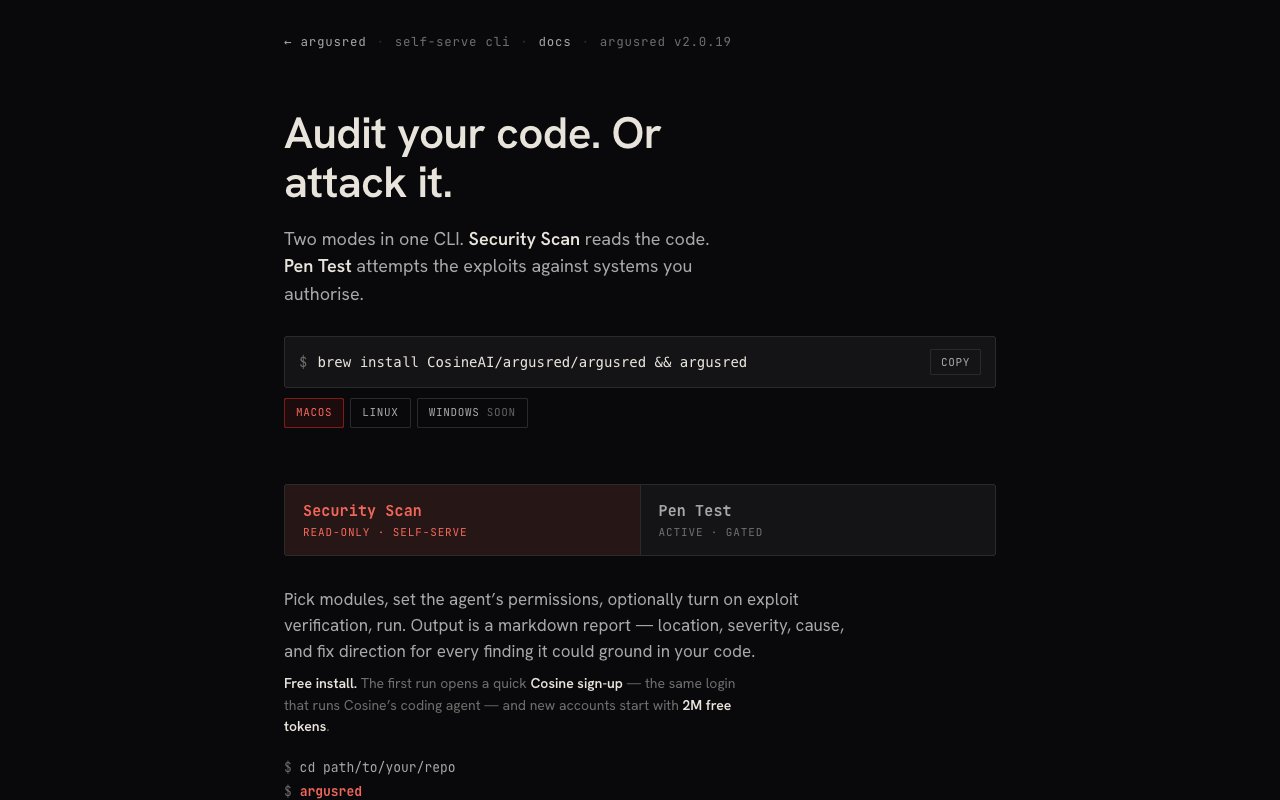
Anthropic and OpenAI's publicly available models are explicitly guard-railed so that they refuse offensive tasks. And their cyber-focussed models are gated for enterprises. This leaves SMEs and mid market open to major vulnerabilities. AI can be used as both an adversarial and defensive tool in the world of cyber. A worst case outcome is if only the adversaries have access. Meanwhile, most existing AI cyber tools are just wrappers. The problem is that they still have all the guardrails on from the foundation model where they will inherit its refusals. For this project we've post-trained a specific model on a decade of capture-the-flag contests. This won't be made available to anyone and everyone, but we do believe that responsible SMEs and midmarket companies also need access to these tools in order to identify key vulnerabilities in their systems; not just enterprises. We have developed two modes that run over a CLI: • Security scan: a read-only audit of your local codebase for vulnerabilities. It only reports what it can tie to a specific file and line, so you're not wading through vibes-based findings. • Pen test: an active adversarial mode that will try to break a live...
Product Data
- Name
- Argusred
- Slug
- argusred
- Website URL
- https://www.argusred.com/cli
- Tagline
- We post-trained a model that pen tests instead of refusing
- Description
- Anthropic and OpenAI's publicly available models are explicitly guard-railed so that they refuse offensive tasks. And their cyber-focussed models are gated for enterprises. This leaves SMEs and mid market open to major vulnerabilities. AI can be used as both an adversarial and defensive tool in the world of cyber. A worst case outcome is if only the adversaries have access. Meanwhile, most existing AI cyber tools are just wrappers. The problem is that they still have all the guardrails on from the foundation model where they will inherit its refusals. For this project we've post-trained a specific model on a decade of capture-the-flag contests. This won't be made available to anyone and everyone, but we do believe that responsible SMEs and midmarket companies also need access to these tools in order to identify key vulnerabilities in their systems; not just enterprises. We have developed two modes that run over a CLI: • Security scan: a read-only audit of your local codebase for vulnerabilities. It only reports what it can tie to a specific file and line, so you're not wading through vibes-based findings. • Pen test: an active adversarial mode that will try to break a live...
- Page title
- argusred — security scan and pen test · ArgusRed
- Meta description
- Audit your code with a read-only Security Scan, or run a gated Pen Test against systems you authorise. Same CLI, two modes. Free on repos you own; pen test by request.
- OG image URL
- https://www.argusred.com/og.png
- Canonical URL
- Not set
- Website status
- live
- HTTP status
- 200
- Last checked at
- Jun 24, 2026